Outpatient clinic management and electronic medical records

Security and audit

Audit trail with an integrity report, enforced password policy, and optional per-user two-factor authentication.

Audit trail and integrity report

Every action is written to an audit trail, and an integrity report checks the trail has not been altered.

Integrity is verified with a hash, not an HMAC, and the rows are not chained. We do not describe the audit trail as immutable.
Password policy

Password rules are applied to every account, and enforced at sign-in.

This is an account-policy control. Nothing beyond that is implied by it.

Optional two-factor authentication

Two-factor authentication is available per user, voluntarily.

It is optional and per-user. It cannot be mandated for everyone by an administrator.

Explore SkyEagle HIS & EMR

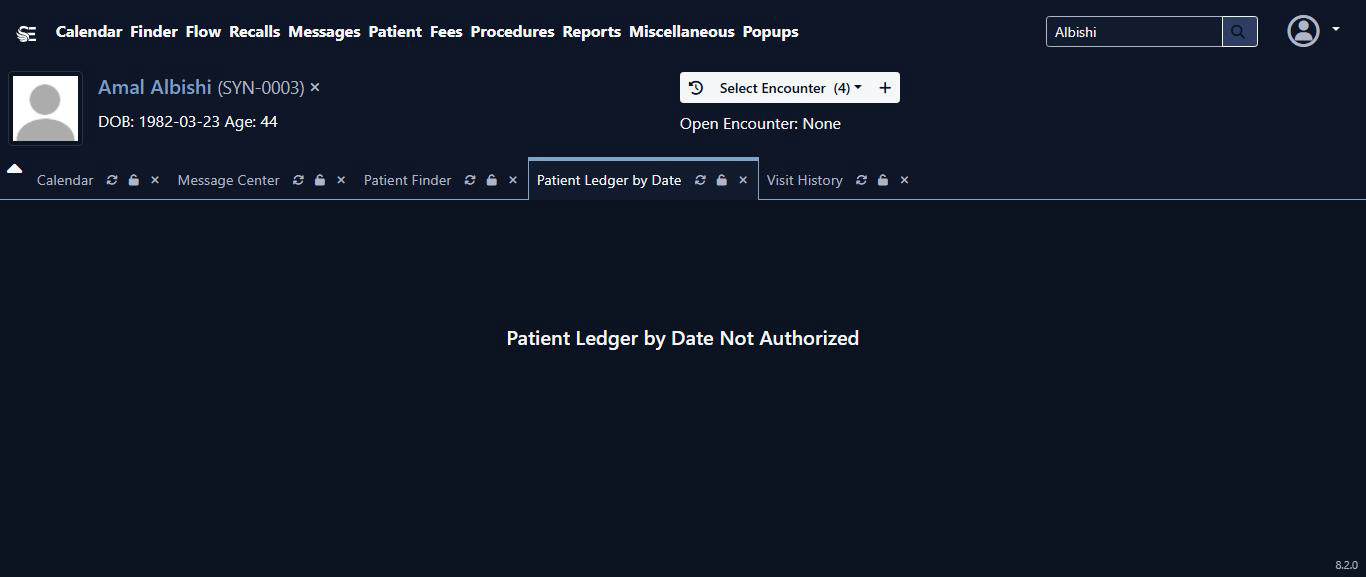
  • Patient Ledger page showing 'Not Authorized' for a clinical support role, rendered in dark theme.
    Access boundaries hold even where you'd least expect to check — clinical staff simply can't see billing.

Captured from the SkyEagle HIS & EMR demonstration environment using synthetic data. No real patient or staff information appears in these images.